Construction Cybersecurity in Canada
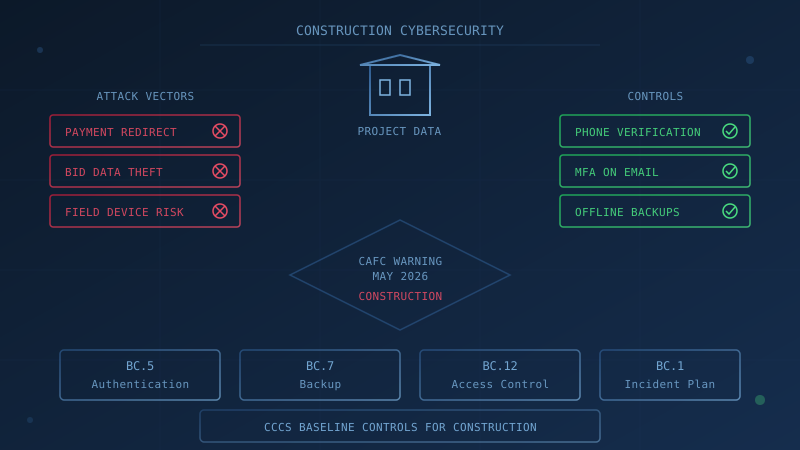
Construction cybersecurity in Canada means protecting the payment processes, project data and field operations that keep general contractors, trades and renovators running. The Canadian Anti-Fraud Centre's May 2026 advisory states that "businesses in the construction and contracting industry, and real estate sector are common targets" for payment redirection fraud. The advisory describes how partners helped recover approximately $3.5 million linked to a fraud targeting a Quebec business that had authorized wire transfers after criminals manipulated email communications. A 2026 Ontario Superior Court decision (Mississippi Mills v. 16442676 CANADA INC, 2026 ONSC 2052) describes how a municipality sent over $201,000 to a fraudulent account after criminals impersonated a construction contractor. This guide covers why construction firms are targeted, what the Canadian Centre for Cyber Security's Baseline Controls recommend, and which practical steps protect against the threats that matter most. This is informational context (not legal advice).
Why Are Construction Companies Targeted by Cybercriminals?
Construction firms hold exactly what criminals want: large payment volumes, multiple parties handling banking details, and tight deadlines that create pressure to act quickly. Three patterns make the industry attractive.
Large Progress Payments and Multiple Parties: Construction projects involve general contractors, subcontractors, suppliers and clients exchanging invoices and payment instructions by email. A single progress draw can reach hundreds of thousands of dollars. The CAFC's May 2026 advisory notes that fraudsters "may impersonate suppliers, contractors, financial institutions or legal representatives to redirect payments or change banking information."
Field Staff and Shared Devices: Workers on job sites access email, project management software and estimating tools from phones, tablets and shared computers. Temporary site offices may rely on portable Wi-Fi. The Canadian Centre for Cyber Security's baseline control BC.8 addresses mobile device security, noting that organizations should "decide on an ownership model for mobile devices and document the rationale and associated risks."
Valuable Project Data: Bid documents, drawings, cost estimates and client contact lists have value. A ransomware attack that encrypts these files and threatens publication creates pressure to pay. A competitor or disgruntled former employee with access to bid pricing can undercut future work.
What Is Construction Cybersecurity and What Does It Involve?
Construction cybersecurity involves the security practices and controls that protect a construction firm's email, project data, financial systems and field operations from cybercrime. For most Canadian construction businesses, the primary threat is fraud: the CAFC's advisory confirms that payment redirection commonly targets the industry. Technical attacks like ransomware also occur, and the same baseline controls that reduce fraud risk also reduce ransomware exposure.
The Baseline Cyber Security Controls for Small and Medium Organizations published by the Canadian Centre for Cyber Security apply to construction firms just as they do to other businesses. The controls are designed for organizations with fewer than 500 employees and are voluntary guidance, not law.
How Does Payment Redirection Fraud Target Construction Businesses?
Payment redirection fraud follows a predictable pattern. An attacker sends an email that appears to come from a trusted subcontractor or supplier, claims the supplier's banking details have changed, and requests a wire transfer to a new account. The CAFC advises businesses to "independently verify payment instructions before sending funds" and to "confirm banking changes using trusted contact information."
The warning signs the CAFC lists include:
- Requests to change or update banking or payment information
- Pressure to act quickly or bypass normal procedures
- Email addresses that closely resemble legitimate ones
- Unexpected wire transfer instructions
- Notices of past-due invoices you have already paid
For construction firms, the risk is amplified by legitimate complexity. Subcontractors do change banks. New suppliers do come onto projects. Progress payments do need to move quickly to keep work on schedule. That legitimate urgency is what attackers exploit.
The single most effective defence is verification through a separate channel: before processing any change to payment details, call the supplier or subcontractor at a phone number you already have on file, not one provided in the request.
Which Security Controls Should a Construction Company Implement?
The Baseline Controls provide a practical framework. Several controls directly address the threats facing construction businesses.
Multi-Factor Authentication (BC.5): BC.5.1 states that "organizations should implement two-factor authentication wherever possible" with priority on "financial accounts, system administrators, cloud administration, privileged users, and senior executives." For a construction firm, that means MFA on email, accounting software, project management platforms and any remote access to company systems. If attackers cannot get into your email, they cannot send fraudulent payment instructions from inside your account.
Backup and Encryption (BC.7): BC.7.1 states that "organizations should back up systems that contain essential business information, and ensure that recovery mechanisms effectively and efficiently restore these systems from back-ups." BC.7.2 requires that "long term backups (e.g. weekly backups) must be stored offline." Project files, estimating data and accounting records must be included. Tested, offline backups are the last line of defence against ransomware.
Access Control (BC.12): BC.12.3 states that "organizations should remove accounts and/or functionality when employees no longer require these for their tasks." Construction workforces include seasonal labourers, project-based hires and subcontractor personnel who may have email accounts, software logins or site access. When their engagement ends, so should their access. Our employee offboarding checklist covers the process.
Mobile Devices (BC.8): The baseline controls note that organizations should "enforce separation between work and personal data on mobile devices with access to corporate IT resources." Field staff using personal phones for work email need clear rules about what apps can access company data and what happens if a phone is lost. See our guide to mobile security and BYOD.
Incident Response Plan (BC.1): BC.1.2 states that "organizations should have a written incident response plan that details who is responsible for handling incidents including any relevant contact information for communicating to external parties, stakeholders and regulators." For a construction firm, the plan should list who calls the bank if a fraud is suspected, who contacts police, and who notifies clients if project data is compromised. See our guide to building an incident response plan.
What Privacy Obligations Apply to Construction Companies?
The Office of the Privacy Commissioner of Canada states that PIPEDA applies to private-sector organizations that collect, use or disclose personal information in the course of commercial activity. For construction firms, this generally covers customer and client personal information collected during commercial projects.
PIPEDA also covers employee personal information, but only for federally regulated businesses such as banks, airlines and telecommunications companies. Most construction companies are provincially regulated employers, so employee records and site access logs are generally governed by provincial employment and privacy law rather than PIPEDA. Construction employers should check their provincial requirements.
In Alberta and British Columbia, the Personal Information Protection Act (PIPA) applies to organizations handling personal information in commercial activity. In Quebec, the Act Respecting the Protection of Personal Information in the Private Sector applies. The OPC states that these provincial laws have been deemed substantially similar to PIPEDA for activities within those provinces.
For reportable breaches, organizations must also notify affected individuals. PIPEDA requires a report to the Office of the Privacy Commissioner when a breach creates a "real risk of significant harm" to an individual. Organizations must keep records of all breaches for at least two years, whether or not they meet the reporting threshold.
What Should a Construction Company Do After a Suspected Attack?
Time matters. If you suspect a payment has been misdirected or your systems have been compromised:
- Contact your bank immediately and request a recall of any fraudulent transfer. The faster you act, the higher the chance of recovery.
- Report to the Canadian Anti-Fraud Centre online at reportcyberandfraud.canada.ca or by phone at 1-888-495-8501. The CAFC advises victims to contact local police and report to the CAFC.
- File a report with local police to create a file number your bank or insurer may require.
- Notify your cyber insurer if you have a policy. Many policies require prompt notification.
- Follow your incident response plan for next steps, including who notifies clients or subcontractors if their information may have been affected.
For detailed reporting guidance, see our guide to how to report a cyber attack in Canada.
Practical Checklist for Construction Cybersecurity
These steps address the threats most relevant to construction businesses:
- Verify banking changes by phone to a number you already have on file, not one provided in the request
- Enable MFA on email and accounting software so attackers cannot send instructions from inside your accounts
- Offboard seasonal workers and subcontractors promptly by removing accounts when their engagement ends
- Set mobile device policies for field staff, including encryption and the ability to wipe company data from lost phones
- Test backups regularly by restoring files to confirm recovery works before you need it
- Train staff on payment verification so accounts payable knows to treat urgent requests with more scrutiny, not less
One Question to Ask Your IT Provider
"Is multi-factor authentication enabled on our email and accounting software, and when did we last test restoring from backup?"
If your IT lead or managed service provider cannot answer this question, that conversation is where your cybersecurity review should start.
Assess Your Construction Company's Cybersecurity
Our free cybersecurity assessment evaluates your organization against the Canadian Centre for Cyber Security's 13 Baseline Control areas. The assessment covers 50 questions, takes under 30 minutes, and is completely confidential. Progress is saved locally for 48 hours. No signup is required. The results show which control areas need attention, so you know where to focus your cybersecurity investment. The assessment is not a compliance audit or legal advice; for those questions, consult a qualified professional.
How prepared is your business?
Find out where you stand against Canada's 13 Baseline Cyber Security Controls. The assessment takes under 30 minutes and your answers stay in your browser.
Check Your ScoreFrequently Asked Questions
Why are construction companies targeted by cybercriminals?
Construction firms handle large progress payments, work with many subcontractors and suppliers, and rely on email to exchange banking details. The Canadian Anti-Fraud Centre's May 2026 advisory states that businesses in the construction and contracting industry are common targets for payment redirection fraud. Project data, bid documents and drawings also have value to competitors or extortionists.
What is payment redirection fraud in construction?
Payment redirection fraud occurs when criminals impersonate a supplier or subcontractor and convince a business to send money to a fraudulent account. The Canadian Anti-Fraud Centre warns that fraudsters may impersonate suppliers, contractors, financial institutions or legal representatives to redirect payments or change banking information. Verifying banking changes by phone to a known number is the primary defence.
What cybersecurity controls should a construction company implement?
The Canadian Centre for Cyber Security's Baseline Controls for Small and Medium Organizations recommend multi-factor authentication wherever possible (BC.5), tested offline backups (BC.7), a written incident response plan (BC.1), and access controls that remove accounts when employees leave (BC.12). For construction firms, this means MFA on email and project management software, mobile device policies for field staff, and offboarding procedures for seasonal workers and subcontractors.
Does PIPEDA apply to construction companies in Canada?
PIPEDA applies to private-sector organizations that collect, use or disclose personal information in the course of commercial activity. For construction firms, this generally means customer and client personal information collected during commercial projects. PIPEDA also applies to employee personal information, but only for federally regulated businesses such as banks, airlines and telecommunications companies. Most construction employers are provincially regulated, so employee records and site access logs are generally governed by provincial employment and privacy law rather than PIPEDA. Firms in Alberta, British Columbia and Quebec are generally covered by substantially similar provincial private-sector privacy law instead of PIPEDA for activities within those provinces.
What should a construction company do after a suspected cyber attack?
Contact your bank immediately and request a recall of any fraudulent payments. Report the incident to the Canadian Anti-Fraud Centre online at reportcyberandfraud.canada.ca or by phone at 1-888-495-8501, and contact your local police. If personal information was exposed and the breach creates a real risk of significant harm, PIPEDA requires a report to the Office of the Privacy Commissioner and notification to affected individuals.
Cite This Page
Suggested citation:
Cybersecurity Canada (2026). Construction Cybersecurity in Canada. Retrieved from https://cybersecuritycanada.ca/news/posts/construction-cybersecurity-canada/
Permanent URL: https://cybersecuritycanada.ca/news/posts/construction-cybersecurity-canada/ · Published November 8, 2026
Disclaimer: This article is intended for general informational purposes only and does not constitute professional cybersecurity, legal, IT, or compliance advice. While we strive to ensure accuracy, the cybersecurity landscape changes rapidly and information may become outdated. Organizations should consult with qualified cybersecurity professionals and legal counsel to assess their specific situation and develop appropriate security policies. Use of this information is at your own risk. See our Privacy Policy for more information.
Cybersecurity Canada is an independent resource and is not affiliated with, endorsed by, or connected to the Canadian Centre for Cyber Security, the Communications Security Establishment, or the Government of Canada.
How does your organization measure up?
Take our free cybersecurity assessment based on the Canadian Centre for Cyber Security's Baseline Controls. 50 questions, under 30 minutes, 100% confidential. Your answers never leave your browser.
Take the Free Assessment