Hospitality Cybersecurity in Canada
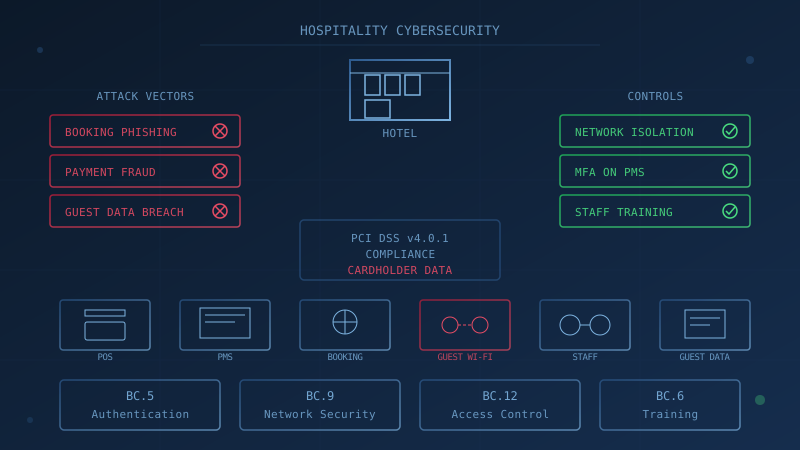
Hospitality cybersecurity in Canada means protecting the payment card data, booking systems and guest information that hotels, motels, bed-and-breakfasts, resorts and restaurants depend on every day. The Canadian Centre for Cyber Security's Baseline Controls state that organizations "should isolate point-of-sale systems from the Internet and other areas of the corporate network with a firewall" (BC.9.6) and that public Wi-Fi "should never connect...to the organization's internal networks or resources." This guide covers why the sector is targeted, what controls apply, and which practical steps matter most. This is informational context (not legal advice).
Why Are Hotels and Hospitality Businesses Targeted?
Hotels and restaurants attract criminals because they combine payment card transactions, guest personal information and internet-connected booking systems.
Payment Card Data: Every card payment involves cardholder data that criminals can monetize. The CCCS Baseline Controls state that organizations "should isolate point-of-sale systems from the Internet and other areas of the corporate network." A POS terminal on the same network as the front desk computer or guest Wi-Fi creates a pathway for attackers who compromise one system to reach payment data.
Booking Platforms: Hotels use online booking engines, channel managers and property management systems (PMS) that handle guest payment details. The Canadian Anti-Fraud Centre's spear phishing page describes how fraudsters send spoofed emails "informing the business of a change in payment details." Booking platform phishing can impersonate guests claiming card issues, or impersonate the platform asking staff to log in.
Staff Turnover: Hospitality has high turnover, including seasonal employees. The CCCS Baseline Controls state that "organizations should remove accounts and/or functionality when employees no longer require these for their tasks" (BC.12.3). Shared front-desk logins defeat this control: you cannot trace who did what or revoke access when one person leaves.
What Payment Card Security Applies to Hospitality?
The PCI Security Standards Council states that PCI DSS applies to "all entities that store, process, or transmit cardholder data (CHD) and/or sensitive authentication data (SAD)," including merchants. If your property accepts Visa, Mastercard, American Express, Discover or JCB, you must comply.
PCI DSS is a contractual requirement from the card brands, not a Canadian statute. Most small hospitality businesses validate compliance through a Self-Assessment Questionnaire (SAQ). A restaurant using a standalone chip terminal via IP would typically use SAQ B-IP. A hotel using a hosted payment page may qualify for SAQ A. Your payment processor determines your specific requirements.
For details, see our guide to PCI DSS for small business in Canada.
How Should Hotels Separate Guest Wi-Fi?
The CCCS Baseline Controls are clear: "if an organization chooses to offer public Wi-Fi services for visitors and guests, the organization should never connect this public network to the organization's internal networks or resources such as printers or audiovisual systems."
Guest Wi-Fi should be on a separate network segment with its own firewall, unable to reach your property management system, POS terminals or back-office computers. A guest device infected with malware should not be able to scan or attack your business systems.
Which CCCS Baseline Controls Apply to Hospitality?
Several Baseline Controls address the threats facing hotels and restaurants.
Multi-Factor Authentication (BC.5): The controls state that "organizations should implement two-factor authentication wherever possible" with priority on "financial accounts, system administrators, cloud administration, privileged users, and senior executives." For a hotel, this means MFA on your PMS, booking engine, channel manager, email and remote access.
Access Control (BC.12): The controls recommend "unique individual accounts" and minimizing "shared or shared-use accounts." Each front-desk employee needs their own login, not a shared "reception" account. When staff leave, access must end that day.
Backup and Encryption (BC.7): Organizations should "back up systems that contain essential business information" and ensure recovery mechanisms work. For a hotel, this includes reservation data, guest records and financial information.
Security Awareness (BC.6): Organizations should "invest in cyber security awareness and training for their employees," covering identification of malicious emails and links. Training should address booking fraud attempts, fake guest complaints and verification procedures.
How Do Frauds Target Hotels?
The CAFC's spear phishing page describes tactics that apply to hospitality. In a "supplier/contractor swindle," fraudsters "send a spoofed email informing the business of a change in payment details" with "new banking information." The CAFC also describes "business executive spoofs" where "a fraudster sends an employee an email that appears to come from the owner, the president or another high-ranking employee."
Hospitality-specific patterns include:
- Fake guests claiming card issues and asking staff to process payment differently
- Emails impersonating booking platforms asking staff to log in
- Suppliers claiming banking details changed
- Requests for refunds to different cards than the original payment
Business email compromise uses similar tactics. The defence is verification: any request to change payment details must be confirmed by phone to a number you already have, not one from the email.
What Privacy Obligations Apply to Hotels?
The Office of the Privacy Commissioner of Canada states that organizations subject to PIPEDA must report breaches of security safeguards involving personal information "that pose a real risk of significant harm to individuals," notify affected individuals, and "keep records of all breaches." The OPC confirms the record-keeping duty covers every breach for at least two years.
The OPC explains that "significant harm includes bodily harm, humiliation, damage to reputation or relationships, loss of employment, business or professional opportunities, financial loss, identity theft, negative effects on the credit record and damage to or loss of property."
Hotels collect guest names, addresses, contact details, payment information and sometimes identification documents. A breach could require notification to the OPC and affected guests.
Provincial laws: In Alberta, British Columbia and Quebec, provincial private-sector privacy laws may apply instead of PIPEDA for activities within those provinces. Quebec's Law 25 requires notification to the Commission d'accès à l'information. Alberta's PIPA requires notification to the Alberta OIPC when there is a real risk of significant harm. BC's PIPA does not currently mandate notification, although the BC OIPC recommends voluntary reporting. Do not mix statutes; check with the relevant provincial privacy commissioner.
What About Vendor Access?
Hotels rely on external vendors: PMS providers, booking engines, payment processors, maintenance contractors. Each creates potential exposure.
The CCCS Baseline Controls state that organizations "should require that all their cloud service providers share an AICPA SSAE 18 SOC 3 report." When vendors need remote access, require MFA and log connections. Our guide to vendor and third-party risk covers assessment without a dedicated security team.
Practical Checklist for Hospitality Cybersecurity
- Isolate guest Wi-Fi from business systems
- Segment POS terminals from office computers
- Enable MFA on booking platforms, PMS and email
- Give each employee their own login
- Remove access the same day when staff leave
- Train staff to verify payment changes by phone to a known number
- Establish a written policy that booking platforms will not ask for login details by email
- Test backups regularly
- Review PCI DSS requirements with your payment processor
What Should You Do After a Suspected Attack?
- Contact your bank and payment processor immediately.
- Isolate affected systems while preserving evidence.
- Report to the Canadian Anti-Fraud Centre at reportcyberandfraud.canada.ca or 1-888-495-8501.
- Contact local police for a file number.
- Assess whether personal information was exposed and determine if notification is required.
- Follow your incident response plan.
For detailed guidance, see how to report a cyber attack in Canada.
One Question to Ask Your IT Provider
"Is our guest Wi-Fi completely separated from our booking and payment systems, and is multi-factor authentication enabled on our PMS and email?"
Assess Your Property's Cybersecurity Posture
Our free cybersecurity assessment evaluates your organization against the Canadian Centre for Cyber Security's 13 Baseline Control areas. The assessment covers 50 questions, takes under 30 minutes, and is completely confidential. Progress is saved locally for 48 hours. No signup is required. The results show which control areas need attention. The assessment is not a PCI DSS assessment, compliance audit or legal advice; for those questions, consult qualified professionals.
How prepared is your business?
Find out where you stand against Canada's 13 Baseline Cyber Security Controls. The assessment takes under 30 minutes and your answers stay in your browser.
Check Your ScoreFrequently Asked Questions
Why are hotels and hospitality businesses targeted by cybercriminals?
Hospitality businesses handle payment card data, collect guest identification, and operate booking platforms connected to the internet. The Canadian Centre for Cyber Security's Baseline Controls recommend isolating point-of-sale systems from the internet and other areas of the corporate network. Staff turnover, seasonal employees and shared front-desk logins create access control challenges. Guest Wi-Fi networks add another attack surface if not properly isolated from business systems.
Does PCI DSS apply to hotels and restaurants in Canada?
Yes. The PCI Security Standards Council states that PCI DSS applies to all entities that store, process, or transmit cardholder data, including merchants such as hotels and restaurants. PCI DSS is a contractual requirement from the card brands, not a Canadian statute. Most small hospitality businesses validate compliance through a Self-Assessment Questionnaire. Your payment processor or acquirer determines your specific validation requirements.
What privacy obligations apply to hotels in Canada?
PIPEDA applies to private-sector organizations that collect personal information in the course of commercial activity. The Office of the Privacy Commissioner states that organizations must report breaches of security safeguards that pose a real risk of significant harm to individuals, notify affected individuals, and keep records of all breaches for two years. In Quebec, British Columbia and Alberta, provincial private-sector privacy laws may apply instead of PIPEDA for activities within those provinces.
How should a hotel separate guest Wi-Fi from business systems?
The Canadian Centre for Cyber Security's Baseline Controls state that if an organization offers public Wi-Fi for visitors and guests, it should never connect this public network to the organization's internal networks or resources. Guest Wi-Fi should be on an isolated network segment with its own firewall, unable to reach reservation systems, point-of-sale terminals or back-office computers.
What should a hospitality business do after a suspected cyber attack?
Contact your bank and payment processor immediately. Report the incident to the Canadian Anti-Fraud Centre online at reportcyberandfraud.canada.ca or by phone at 1-888-495-8501, and file a report with local police. If personal information was exposed and the breach creates a real risk of significant harm, organizations subject to PIPEDA must report to the Office of the Privacy Commissioner and notify affected individuals.
Cite This Page
Suggested citation:
Cybersecurity Canada (2026). Hospitality Cybersecurity in Canada. Retrieved from https://cybersecuritycanada.ca/news/posts/hospitality-cybersecurity-canada/
Permanent URL: https://cybersecuritycanada.ca/news/posts/hospitality-cybersecurity-canada/ · Published November 12, 2026
Disclaimer: This article is intended for general informational purposes only and does not constitute professional cybersecurity, legal, IT, or compliance advice. While we strive to ensure accuracy, the cybersecurity landscape changes rapidly and information may become outdated. Organizations should consult with qualified cybersecurity professionals and legal counsel to assess their specific situation and develop appropriate security policies. Use of this information is at your own risk. See our Privacy Policy for more information.
Cybersecurity Canada is an independent resource and is not affiliated with, endorsed by, or connected to the Canadian Centre for Cyber Security, the Communications Security Establishment, or the Government of Canada.
How does your organization measure up?
Take our free cybersecurity assessment based on the Canadian Centre for Cyber Security's Baseline Controls. 50 questions, under 30 minutes, 100% confidential. Your answers never leave your browser.
Take the Free Assessment