Cybersecurity for Healthcare Clinics in Canada
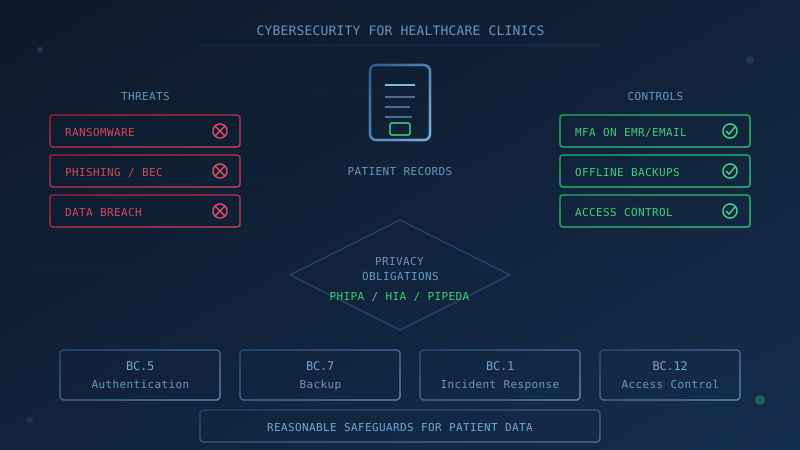
Ontario's Information and Privacy Commissioner reported 12,075 breaches of personal health information in 2025, up from 11,970 in 2024. Misdirected faxes alone accounted for 5,438 (45%) of those breaches. For Canadian healthcare clinics, including small medical practices, dental clinics, physiotherapy offices, and similar private health settings, cybersecurity for healthcare clinics in Canada means implementing reasonable safeguards under provincial health privacy law and the practical controls that protect patient data from theft, ransomware, and fraud. This guide covers which privacy laws apply, what safeguards regulators require, and which controls to implement first. This is informational context (not legal advice); check your own provincial privacy commissioner and professional college guidance.
Why Are Healthcare Clinics Targets for Cyberattacks?
Healthcare clinics hold exactly what cybercriminals want: sensitive personal health information, financial data, and access to interconnected systems. Three patterns make private clinics attractive targets.
Sensitive Data That Cannot Be Changed: Patient records contain names, dates of birth, health card numbers, diagnoses, and treatment histories. Unlike a credit card number, a health history cannot be reissued. A clinic that loses access to patient records through ransomware cannot operate until systems are restored, and attackers know this creates pressure to pay.
Limited IT Resources: Small clinics may not have dedicated IT staff. Electronic medical record (EMR) and practice management systems are networked and internet-connected, but security monitoring and patching may be sporadic. This matches the profile CCCS designed the Baseline Controls to address: organizations under 500 employees facing cybercrime as their primary threat.
Multiple Entry Points: Clinics handle email, online booking, payment processing, insurance claims, and EMR access. Each is a potential entry point. Business email compromise and phishing remain common attack methods, and clinic staff may receive fraudulent requests that appear to come from patients, insurers, or suppliers.
Which Privacy Law Applies to Your Clinic?
The privacy law that applies to your clinic depends on your province. The Office of the Privacy Commissioner of Canada states that "determining which law applies must be done on a case-by-case basis."
Ontario: The Personal Health Information Protection Act, 2004 (PHIPA) applies to health information custodians, including physicians, dentists, chiropractors, physiotherapists, pharmacists, and other regulated health professionals. Section 12(1) of PHIPA states: "A health information custodian shall take steps that are reasonable in the circumstances to ensure that personal health information in the custodian's custody or control is protected against theft, loss and unauthorized use or disclosure and to ensure that the records containing the information are protected against unauthorized copying, modification or disposal."
Alberta: The Health Information Act applies to custodians of health information. Section 60(1) states that "a custodian must take reasonable steps in accordance with the regulations to maintain administrative, technical and physical safeguards" that protect the confidentiality of health information and the privacy of individuals. Sections 60.1(2) and (3) require that when a breach creates a risk of harm, notice must be given "as soon as practicable" to the Commissioner, the Minister, and the affected individual. The OIPC Alberta is the regulator responsible for ensuring compliance.
Other Provinces: Provincial health privacy laws vary. The OPC states that Ontario, New Brunswick, Nova Scotia, and Newfoundland and Labrador have health information laws deemed substantially similar to PIPEDA. In provinces without substantially similar legislation, PIPEDA may apply to commercial activity involving personal information. Check with your provincial privacy commissioner.
What Breach Reporting Does Your Province Require?
Ontario: The IPC Ontario requires notification of certain breaches at the first reasonable opportunity under subsection 12(3) of PHIPA. The IPC lists seven categories requiring notification, including unauthorized use or disclosure where the person "knew or should have known" the action was not permitted, stolen information, patterns of similar breaches, and significant breaches. Additionally, all health information custodians must submit annual breach statistics to the IPC by March 1 each year, covering all breaches from the previous calendar year, regardless of whether they were individually reported.
Alberta: Sections 60.1(2) and (3) of the Health Information Act require that when a breach creates a risk of harm, notice must be given "as soon as practicable" to the Commissioner, the Minister, and the affected individual. The OIPC Alberta states that "custodians are required to notify the Commissioner of such breaches as soon as practicable."
PIPEDA: Where PIPEDA applies, organizations must report breaches creating a "real risk of significant harm" to the Office of the Privacy Commissioner of Canada and notify affected individuals. See our guide to Canada's privacy landscape.
Which Security Controls Should a Healthcare Clinic Implement?
The Canadian Centre for Cyber Security's Baseline Cyber Security Controls for Small and Medium Organizations provides a practical framework. Several controls directly address the threats facing healthcare clinics.
Multi-Factor Authentication (BC.5): BC.5.1 states that "organizations should implement two-factor authentication wherever possible" and that "organizations should require two-factor authentication for important accounts such as financial accounts, system administrators, cloud administration, privileged users, and senior executives." For a clinic, that means MFA on email, EMR and practice management systems, and any remote access. No shared front-desk logins: each staff member should have their own account with MFA enabled.
Access Control (BC.12): BC.12.1 states that "organizations should provision accounts with the minimum functionality necessary for tasks." BC.12.3 states that "organizations should remove accounts and/or functionality when employees no longer require these for their tasks." For a clinic, this means reception staff should not have the same EMR access as clinicians, and accounts should be revoked promptly when staff leave. See our employee offboarding checklist.
Backup and Encryption (BC.7): BC.7.1 states that "organizations should back up systems that contain essential business information, and ensure that recovery mechanisms effectively and efficiently restore these systems from back-ups." BC.7.2 requires that "long term backups (e.g. weekly backups) must be stored offline." Tested, offline backups are the last line of defence against ransomware. If your backups are only on a network-connected drive, ransomware can encrypt them too. See our guide to backup and recovery.
Incident Response Plan (BC.1): BC.1.2 states that "organizations should have a written incident response plan that details who is responsible for handling incidents including any relevant contact information for communicating to external parties, stakeholders and regulators." For a clinic, the plan should address how to notify the privacy commissioner, affected patients, insurers, and your professional college if required. See our guide to building an incident response plan.
What Questions Should You Ask Your EMR Vendor?
Your EMR and practice management systems are critical infrastructure. The CCCS Baseline Control BC.10 addresses cloud and outsourced IT services. Questions to ask your vendor:
- Does the system require multi-factor authentication for all users?
- How are backups performed, and can we restore from them if needed?
- Where is our data stored, and who has access?
- What is your notification process if you experience a breach?
- Do you provide a SOC 2 or SOC 3 report demonstrating security practices?
These questions apply whether your EMR is cloud-hosted or on-premises with vendor support. See our guide to vendor and third-party risk.
What Staff Training Does a Clinic Need?
BC.6.1 of the Baseline Controls states that "organizations should invest in cyber security awareness and training for their employees." For healthcare clinics, training should cover:
- How to recognize phishing emails and fraudulent requests
- Why shared passwords create risk (and why each staff member needs their own login)
- What to do if they suspect a breach or receive a suspicious message
- How to handle patient information securely, including avoiding misdirected faxes and emails
The IPC Ontario's 2025 statistics found that misdirected faxes accounted for 45% of reported health privacy breaches. Staff awareness directly reduces this category of breach.
One Question to Ask Your IT Provider
"Is multi-factor authentication enabled on our email, EMR, and practice management systems, and when was our last backup restoration test?"
If your IT lead or managed service provider cannot answer this question, that conversation is where your cybersecurity review should start. The controls that matter most for a clinic are the ones that protect patient data and keep your practice running.
Assess Your Clinic's Cybersecurity Posture
Our free cybersecurity assessment evaluates your organization against the Canadian Centre for Cyber Security's 13 Baseline Control areas. The assessment covers 50 questions, takes under 30 minutes, and your answers stay in your browser. Progress is saved locally for 48 hours. No signup is required. The results show which control areas need attention, so you know where to focus your cybersecurity investment. The assessment is not a privacy impact assessment or a PHIPA compliance audit; for compliance questions, consult your provincial privacy commissioner and your professional college.
How prepared is your business?
Find out where you stand against Canada's 13 Baseline Cyber Security Controls. The assessment takes under 30 minutes and your answers stay in your browser.
Check Your ScoreFrequently Asked Questions
What privacy law applies to healthcare clinics in Canada?
It depends on the province. In Ontario, the Personal Health Information Protection Act, 2004 (PHIPA) applies to health information custodians. In Alberta, the Health Information Act applies. In British Columbia, Quebec, and other provinces, provincial health privacy laws or the federal PIPEDA may apply depending on the circumstances. The Office of the Privacy Commissioner of Canada states that determining which law applies must be done on a case-by-case basis.
What does PHIPA require for clinic security?
Section 12(1) of PHIPA states that a health information custodian shall take steps that are reasonable in the circumstances to ensure that personal health information in the custodian's custody or control is protected against theft, loss and unauthorized use or disclosure and to ensure that the records containing the information are protected against unauthorized copying, modification or disposal.
Do Ontario clinics have to report breaches?
Yes. Under PHIPA, health information custodians must notify the Information and Privacy Commissioner of Ontario and affected individuals of certain privacy breaches. Custodians must also submit annual breach statistics to the IPC by March 1 each year, regardless of whether those breaches were individually reported.
What cybersecurity controls should a clinic implement?
The Canadian Centre for Cyber Security's Baseline Controls for Small and Medium Organizations recommend multi-factor authentication (BC.5), tested offline backups (BC.7), a written incident response plan (BC.1), and access controls that remove accounts when employees leave (BC.12). These controls directly address the threats facing healthcare clinics.
Why are healthcare clinics targeted by cybercriminals?
Healthcare clinics hold sensitive personal health information that cannot be changed or reissued, unlike a credit card. Clinics may have limited IT resources, rely on electronic medical record systems with network access, and handle financial transactions. Ransomware attackers know that a clinic unable to access patient records cannot operate, which creates pressure to pay.
Cite This Page
Suggested citation:
Cybersecurity Canada (2026). Cybersecurity for Healthcare Clinics in Canada. Retrieved from https://cybersecuritycanada.ca/news/posts/cybersecurity-for-healthcare-clinics-in-canada/
Permanent URL: https://cybersecuritycanada.ca/news/posts/cybersecurity-for-healthcare-clinics-in-canada/ · Published November 1, 2026
Disclaimer: This article is intended for general informational purposes only and does not constitute professional cybersecurity, legal, IT, or compliance advice. While we strive to ensure accuracy, the cybersecurity landscape changes rapidly and information may become outdated. Organizations should consult with qualified cybersecurity professionals and legal counsel to assess their specific situation and develop appropriate security policies. Use of this information is at your own risk. See our Privacy Policy for more information.
Cybersecurity Canada is an independent resource and is not affiliated with, endorsed by, or connected to the Canadian Centre for Cyber Security, the Communications Security Establishment, or the Government of Canada.
How does your organization measure up?
Take our free cybersecurity assessment based on the Canadian Centre for Cyber Security's Baseline Controls. 50 questions, under 30 minutes, 100% confidential. Your answers never leave your browser.
Take the Free Assessment